

👾 I tell computer what to do, Tech Blogger, MVP (Most Valuable Papa)
Help me reach 1K subs 🥹 👉
Joined July 2009
- Tweets1K
- Following68
- Followers367
- Likes2



Pinned Tweet
Help me reach 1K subs before 2027 🥹 👉 youtube.com/@juniandev
Thank you!


YouTube is making changes to the YouTube Partner Program (YPP) for *new* applicants.
Starting February 1, 2027, creators will need:
1. 8000 Qualified Watch Hours (up from 4000), or
2. 20M Qualified Shorts Views (up from 10M)
There are no eligibility changes for fan funding.

ALT Starting Feb. 1, 2027, YPP entry thresholds for new applicants are changing to 8,000 qualified watch hours in the last 365 days, or 20M qualified Shorts views in the last 90 days. There are no changes to the eligibility requirements to gain access to fan funding features (ex: Super Chats & channel memberships), YouTube Creator Partnerships, or YouTube Shopping. These products will continue to help creators to start their earning journeys even earlier when they reach 500 subscribers and either 3,000 qualified watch hours in the last 365 days or 3M qualified Shorts views in the last 90 days.


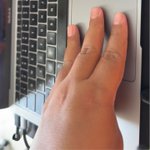
I'm doing a three-finger salute every single day on my trackpad.
I hope this regime is dethroned very soon and replaced with something more reliable.

junian.dev retweeted
I stopped keep up with Apple news as soon I can't afford any of the new hardware
PCB juga kena 😭

AI demand triggers massive PCB shortage for PC makers as order books full until 2030 — lead times stretch to 30 months as material costs surge 12x tomshardware.com/pc-componen…

junian.dev retweeted

Selamat pagi terutama para buzzer IQ dibawah 78.
Tonton nih clip The Hunger Games.
Three finger salute itu simbol solidaritas dan perlawanan atas kekuasaan yang menindas.
Makanya perbanyak wawasan jangan keseringan baca script orderan doang. 😂


The ship name is “Odyssey”.
What did you expect? Of course you’re gonna be stranded. It’s part of the attraction.

'Cruise for life' passengers stranded.
Around 200 passengers who paid to live on a cruise ship while travelling the world were abruptly left in a Cambodian port after the company ran out of money
u.afp.com/SycR


junian.dev retweeted

EBITDA = Earnings Before I Trick Da Auditor

Anthropic has filed an S-1 registration statement with the SEC related to its proposed IPO.
Read more: anthropic.com/news/s1-sec
Legal disclaimer: A registration statement relating to these securities has been filed with the SEC but has not yet become effective. These securities may not be sold, nor may offers to buy be accepted, prior to the time the registration statement becomes effective. This post does not constitute an offer to sell or the solicitation of an offer to buy these securities, nor shall there be any sale of these securities in any state or jurisdiction in which such offer, solicitation or sale would be unlawful prior to registration or qualification under the securities laws of any such state or jurisdiction.

I never get the appeal of foldable phones. It looks fragile, and you can always notice the crease.
If it’s designed like a Nintendo DS then I may have some interest.

It took about five minutes for Jesse Dalton’s iPhone Duo dream to shift into nightmare mode.
He had only opened and closed the Duo four or five times when the hinge got stuck at a 45-degree angle. Dalton tried to pry it open and heard a loud pop.
🔗 on.wsj.com/3UrzwNd

Updated to macOS 27.2, and it's still using the compromised eMudhra CA. Hey @Apple, make this priority, please.


For anyone using macOS and doesn't want to edit /etc/ssl/cert.pem for eMudhra fix, you can also use ca-certificates from Mozilla through Homebrew.
Details here: junian.dev/blog/mac-curl-cus…


PSA for macOS users:
1. Apple’s supplied SSL certificate bundle at /etc/ssl/cert.pem still trusts certificates attackers can forge using compromised eMudhra keys.
2. I confirmed this on macOS 26.7.1 and 27.0.1 using Apple’s built-in curl and Git.
3. An attacker intercepting connections from tools using this bundle could replace downloads with malware. With commands like curl … | sh, that malware would execute immediately.
4. Removing the roots that authorize those certificates blocks the tested chains. Both OS updates restored roots I’d previously removed, requiring me to remove them again.
4. I’ve submitted the findings to Apple’s security team and am awaiting their response. In the meantime, you can apply a temporary fix as outlined below.
5. To check and fix your machine, give an agent like ChatGPT/Codex or Claude Code the following prompt:
“Independently verify whether Apple’s /etc/ssl/cert.pem still permits trust in certificates signed with compromised eMudhra keys. If so, back it up and remove the roots enabling that trust, identified by verified SPKI fingerprints. Confirm Apple’s built-in curl and Git reject those chains while ordinary HTTPS still works. Preserve rollback and never disable TLS verification.”
Note that removing these roots can also block legitimate sites. This is a temporary mitigation, not a substitute for a fix from Apple.
I’ll share the script I used in a follow-up post if you’d prefer to use that directly.
Here's my temporary eMudhra fix for git on macOS.
Details here: junian.dev/blog/mac-git-cust…


If I’d known working in IT would be this stressful, especially post-AI era, I probably wouldn’t have studied CS in the past.
I should’ve worked as a finance bro or something.
