

Technologist,Atheist,rationalist,empiricist and non-believer in unicorns, virgin births or https://nitter.cf/t.co/JWGHmFcFSn Linux,Science,Wine and the Arts @codfather.bsky.so
London,La Loire & Almeria
Joined January 2009
- Tweets54.7K
- Following18.3K
- Followers16.7K
- Likes102K




codfather #FBPE 🇪🇺🇫🇷 🏴🇺🇦 retweeted
😂 I bet the daft fuckers will try and find them on the high street to ignore them - lol
codfather #FBPE 🇪🇺🇫🇷 🏴🇺🇦 retweeted

The once sure-footed Reform leader is struggling badly after a summer of horrible headlines and plummeting polls
✍️ Rats in a Sack 🐀
buff.ly/OStkyai

codfather #FBPE 🇪🇺🇫🇷 🏴🇺🇦 retweeted
What GoAhead is and the devices that use it: embedthis.com/goahead/

codfather #FBPE 🇪🇺🇫🇷 🏴🇺🇦 retweeted

To be absolutely clear, I am happy for people to like Tommy Robinson posts, provided they delete their entire social media history if they want to become a Reform candidate. Being a far right scumbag is fine, provided you hide it until we get into power.
codfather #FBPE 🇪🇺🇫🇷 🏴🇺🇦 retweeted

Think of this....... before Bonfire night
- Bolsanaro has lost in Brazil
- the Student List took Serbia
- Tommy Robinson could well be sent down
- Standards will find Farage guilty
- Netanyahu will likely lose
- Trump will be screwed in the mid terms
Interesting time to be alive


codfather #FBPE 🇪🇺🇫🇷 🏴🇺🇦 retweeted
😂

Very cool, entertaining and with high production values: if I were @Nigel_Farage, I’d consider dipping into that £5 million to try to get out a video that can compare to it.


codfather #FBPE 🇪🇺🇫🇷 🏴🇺🇦 retweeted

Still not aliens, but one of the weirdest things we have found in a sky where weird things are not in short supply. iflscience.com/one-radio-sou…

codfather #FBPE 🇪🇺🇫🇷 🏴🇺🇦 retweeted

Ubuntu 26.10 is now available for download, with GNOME 51, Linux 7.3 and new desktop features – including a slick new way to quickly tile app windows! #ubuntu

codfather #FBPE 🇪🇺🇫🇷 🏴🇺🇦 retweeted
Ubuntu 26.04 LTS has been released. The latest long-term support release gets 5 years of updates, but is the first LTS to not include an X11/Xorg desktop session.

ALT Bento design shows features in Ubuntu 26.04 LTS.
codfather #FBPE 🇪🇺🇫🇷 🏴🇺🇦 retweeted
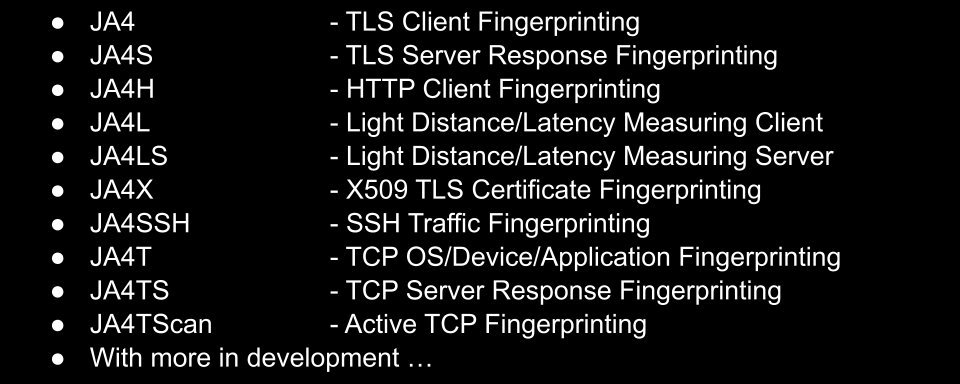
Announcing 3 Critical vulns for hundreds of millions of IoT, Firewalls, OT, and Military devices including: Palo Alto Networks, Comcast, D-Link, HP, Canon, Honeywell, GE, Oracle, Siemens, Rockwell, Digi, Lockheed Martin, Boeing...
The vulns are with GoAhead Web Server which is a backend library used by these devices. There's a patch available from GoAhead but that doesn't mean there's a patch available for the devices yet -- that's up to the manufacturer.
- TLS traffic over DHE ciphers have a 1-byte secret, "04", meaning anyone can decrypt connections to these devices and steal login credentials and session tokens if the client negotiated with DHE ciphers like the latest TLS_DHE_RSA_WITH_CHACHA20_POLY1305_SHA256, which is extremely likely.
- LibreSSL mTLS has been completely bypassed, meaning anyone can connect over mTLS. If you have one of these devices listening on the internet and are expecting mTLS to protect it from attackers, take it offline or patch asap.
- OpenSSL Certificate Revocation Lists (CRLs) are not enforced, meaning if a user device is stolen or compromised, and you revoke that mTLS cert, nothing actually happens. There are a lot of other attacks this can be used for.
These are critical because these types of devices run our world. Water systems, electricity, military, firewalls, critical infrastructure.
foxio.io/blog/choose-your-ba…

codfather #FBPE 🇪🇺🇫🇷 🏴🇺🇦 retweeted

Firefox 159 Released With AMD Linux Graphics Fix For Excessive Memory Use
phoronix.com/news/Firefox-15…

codfather #FBPE 🇪🇺🇫🇷 🏴🇺🇦 retweeted
Linux 7.4 Expands Sensor Monitoring For More @ASUSUSA & @msigaming Motherboards, New @Hi_MINISFORUM Driver
phoronix.com/news/Linux-7.4-…


codfather #FBPE 🇪🇺🇫🇷 🏴🇺🇦 retweeted

Never check a role name in your code
In one of the projects where I worked, we had role checks in many places across the project. Then, we needed to introduce a new role and that was a cumbersome code change in many places.
RBAC stands for Role-Based Access Control. The path we selected was to give users roles and let the code ask "is this user a Manager?"
Yet, the model has one more part. Users get roles, roles get permissions and permissions define what a user can do.
The code should only ask about the permission, for example "can this user approve an invoice?"
Here is the complete flow:
𝟭. 𝗧𝗵𝗲 𝘁𝗼𝗸𝗲𝗻 𝗰𝗮𝗿𝗿𝗶𝗲𝘀 𝗿𝗼𝗹𝗲𝘀. We set up the identity provider to add them at sign-in.
𝟮. 𝗧𝗵𝗲 𝗔𝗣𝗜 𝘁𝘂𝗿𝗻𝘀 𝗿𝗼𝗹𝗲𝘀 𝗶𝗻𝘁𝗼 𝗽𝗲𝗿𝗺𝗶𝘀𝘀𝗶𝗼𝗻𝘀. It reads the mapping from its database and keeps a short cache.
𝟯. 𝗧𝗵𝗲 𝗲𝗻𝗱𝗽𝗼𝗶𝗻𝘁 𝗰𝗵𝗲𝗰𝗸𝘀 𝗼𝗻𝗲 𝗽𝗲𝗿𝗺𝗶𝘀𝘀𝗶𝗼𝗻. It asks for invoices:approve and never names a role.
𝟰. 𝗔𝗻 𝗮𝗱𝗺𝗶𝗻 𝗮𝗱𝗱𝘀 𝗮 𝗻𝗲𝘄 𝗿𝗼𝗹𝗲 𝗮𝘀 𝗱𝗮𝘁𝗮. The admin creates the Auditor role in the identity provider. One table row maps it to invoices:read. The code stays the same, and nothing gets deployed.
In ASP.NET Core, the endpoint gets [Authorize(Policy = "invoices:approve")]. It replaces [Authorize(Roles = "Manager")]. Behind it, a policy provider turns that name into a requirement. A handler checks it against the user's permissions.

ALT Sequence diagram: RBAC, check permissions, not roles. The token carries roles, the API maps roles to permissions, the endpoint checks one permission.

