

Malware researcher, CEH, GREM, electronics geek, IoT enthusiast, programmer, drone lover and machine learning fan. Just hunting malware for fun... and profit!
Bogotá, D.C., Colombia
Joined August 2017
- Tweets1.7K
- Following736
- Followers2.8K
- Likes1.9K


Felipe Duarte retweeted

Andrew Ng just dropped the best 2-hour course on Graph Engineering: from single agent to full automation
9:14 - your first agent
33:11 - loop engineering
1:02:46 - graph engineering
1:30:15 - agents that rewrite themselves
1:49:05 - full graph system
two hours, and it replaces every agent tutorial you bookmarked this year
Prompts → Agents → Loops → Graphs
most people will stop after the first agent and call it automation
he saves the last forty minutes for the graph that runs it without him
same model, same tokens, completely different week
watch it today
the step-by-step guide is below, save it while it is still early ↓


Felipe Duarte retweeted

I built an open-source library of 700+ cybersecurity skills for AI coding agents -- covers DFIR, threat hunting, cloud security, and more github.com/mukul975/Anthropi…

Felipe Duarte retweeted

Agentic-SOC-Simulation: AI-powered SOC simulation platform github.com/SafelineMan/Agent…


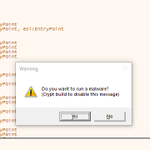
Things that you only see in malware analysis 🤯
I just unpacked Lumma Stealer, and the first sign to know I nailed it: a warning pop up!
A debug message to remind rookie attackers not to self-infect 😂
#MalwareAnalysis #Cybersecurity


Check out! Our latest research were we exposed several tools found during an incident response involving APT41.
securityjoes.com/post/the-si…


Felipe Duarte retweeted

You can also leverage @virustotal Enterprise to search for potential C2s related to #LummaC2 based on the redirect page.


Felipe Duarte retweeted

Quick changes on this reCAPTCHA malware campaign now abusing @digitalocean S3 buckets and CDN to still deliver #Lumma Stealer.
Similar behavior,
Detonation: app.any.run/tasks/02afc68d-6…


reCAPTCHA malware campaign is now abusing @Vultr S3 buckets and CDN to deliver #Lumma Stealer
Detonation:
app.any.run/tasks/ccf381f1-3…
Also loading another unidentified binary from /onefreex.com/api/download that only downloads with a custom User Agent: app.any.run/tasks/d9d21810-8…


Felipe Duarte retweeted

#Lummac2
With this simple query is possible to find more Lumma C2:
urlscan.io/search/#hash%3A51…
CC:
@banthisguy9349 @NDA0E @BlinkzSec @kddx0178318 @raghav127001 @DaveLikesMalwre @g0njxa @ViriBack @500mk500 @ge0lev


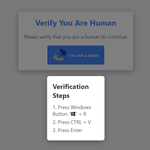
¡Atención! 🚩 Están circulando campañas de distribución del malware Lumma Stealer, usando una técnica tan simple (y estúpida) como peligrosa. Esta campaña afecta especialmente en sitios de streaming llenos de anuncios.


Los atacantes están usando falsos CAPTCHA para engañarte. Te piden presionar "Win + R", luego "CTRL + V" y Enter, haciendo que ejecutes tú mismo un comando de PowerShell que descarga el malware. 🤦♂️
Muchas herramientas de seguridad no logran detener el ataque y tu máquina termina infectada. ¡Cuidado con lo que haces! #Ciberseguridad #Malware #Phishing
Felipe Duarte retweeted
MSIX is still so hot right now, here is the basic query to get started with some juicy malware hunting, thanks @urlscanio 🕵️
query: page.url:".msix" NOT page.url:*statics.teams* NOT page.url:*teams.static*

Felipe Duarte retweeted

📢¡¡El CFP del BlueSpace explota!!📢
Gracias a todos por mandar sus propuestas. Este año recibimos tantas charlas que decidimos 𝐚𝐝𝐞𝐥𝐚𝐧𝐭𝐚𝐫 𝐥𝐚 𝐟𝐞𝐜𝐡𝐚 𝐝𝐞 𝐜𝐢𝐞𝐫𝐫𝐞 𝐝𝐞𝐥 𝐜𝐟𝐩 𝐚 𝐞𝐬𝐭𝐞 𝐯𝐢𝐞𝐫𝐧𝐞𝐬 𝟒/𝟏𝟎 ‼️
¡Vamos! ¡Vamos! 👉 forms.gle/pnNJcBDkHBh16m1c9