

Malware researcher, CEH, GREM, electronics geek, IoT enthusiast, programmer, drone lover and machine learning fan. Just hunting malware for fun... and profit!
Bogotá, D.C., Colombia
Joined August 2017
- Tweets1.7K
- Following736
- Followers2.8K
- Likes1.9K


Felipe Duarte retweeted

Andrew Ng just dropped the best 2-hour course on Graph Engineering: from single agent to full automation
9:14 - your first agent
33:11 - loop engineering
1:02:46 - graph engineering
1:30:15 - agents that rewrite themselves
1:49:05 - full graph system
two hours, and it replaces every agent tutorial you bookmarked this year
Prompts → Agents → Loops → Graphs
most people will stop after the first agent and call it automation
he saves the last forty minutes for the graph that runs it without him
same model, same tokens, completely different week
watch it today
the step-by-step guide is below, save it while it is still early ↓


Felipe Duarte retweeted

I built an open-source library of 700+ cybersecurity skills for AI coding agents -- covers DFIR, threat hunting, cloud security, and more github.com/mukul975/Anthropi…

Felipe Duarte retweeted

Agentic-SOC-Simulation: AI-powered SOC simulation platform github.com/SafelineMan/Agent…


Felipe Duarte retweeted

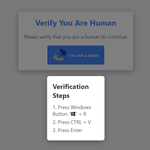
You can also leverage @virustotal Enterprise to search for potential C2s related to #LummaC2 based on the redirect page.


Felipe Duarte retweeted

Quick changes on this reCAPTCHA malware campaign now abusing @digitalocean S3 buckets and CDN to still deliver #Lumma Stealer.
Similar behavior,
Detonation: app.any.run/tasks/02afc68d-6…


reCAPTCHA malware campaign is now abusing @Vultr S3 buckets and CDN to deliver #Lumma Stealer
Detonation:
app.any.run/tasks/ccf381f1-3…
Also loading another unidentified binary from /onefreex.com/api/download that only downloads with a custom User Agent: app.any.run/tasks/d9d21810-8…


Felipe Duarte retweeted

#Lummac2
With this simple query is possible to find more Lumma C2:
urlscan.io/search/#hash%3A51…
CC:
@banthisguy9349 @NDA0E @BlinkzSec @kddx0178318 @raghav127001 @DaveLikesMalwre @g0njxa @ViriBack @500mk500 @ge0lev


Felipe Duarte retweeted
MSIX is still so hot right now, here is the basic query to get started with some juicy malware hunting, thanks @urlscanio 🕵️
query: page.url:".msix" NOT page.url:*statics.teams* NOT page.url:*teams.static*

Felipe Duarte retweeted

📢¡¡El CFP del BlueSpace explota!!📢
Gracias a todos por mandar sus propuestas. Este año recibimos tantas charlas que decidimos 𝐚𝐝𝐞𝐥𝐚𝐧𝐭𝐚𝐫 𝐥𝐚 𝐟𝐞𝐜𝐡𝐚 𝐝𝐞 𝐜𝐢𝐞𝐫𝐫𝐞 𝐝𝐞𝐥 𝐜𝐟𝐩 𝐚 𝐞𝐬𝐭𝐞 𝐯𝐢𝐞𝐫𝐧𝐞𝐬 𝟒/𝟏𝟎 ‼️
¡Vamos! ¡Vamos! 👉 forms.gle/pnNJcBDkHBh16m1c9
Felipe Duarte retweeted

Anders Olsson’s and my talk from Security Fest.
Get insights how VMware/ESXi ransomware works, how to recover, how to do incident response and how to protect for it. Also how Captain Underpants can assist in Threat Intelligence.
m.youtube.com/watch?v=Z7pmI7…
#Truesec

Felipe Duarte retweeted

#MasterParser highlights and consolidates similar & relevant threat-related #Linux logs, showing what matters, instead of garbage logs.
It will also calculates timestamps and measures timeline activities, focusing on anomaly detection.
#DFIR #MalwareAnalysis #LateralMovement #OpenSource
👏🏻👏🏻👏🏻

Felipe Duarte retweeted
The recent intrusion from #SocGholish infection we have observed at @esthreat
If you see your email signatures are being replaced by:
✅ file://170.130.55[.]72/logocompany.jpeg
✅ file://170.130.55[.]72/main_logo.png
Please isolate the host immediately 🚨
Article: esentire.com/blog/socgholish…

Felipe Duarte retweeted
Threat Researcher, Eilay Yosfan, got accepted to @BlackHatEvents to present MasterParser #DFIR open-source tool 🎉🎉🎉
See you there !!

Felipe Duarte retweeted

🔒 Login panel #Amadey #Stealer
🌐 #opendir: 62.204.41[.78
💻 Panel URL: 62.204.41[.78/8BvxwQdec3/
🔍 Query to @urlscanio:
page.url:"8BvxwQdec3"
📡 Other:
194.116.215[.177/8BvxwQdec3/

Felipe Duarte retweeted

Because writing detection rules for new emerging and #APT trends is an integral part of our work as #malware|#threat researchers, I created and cooked these #YARA rules for the initial stage dropper of the non-attributed APT group duped #DuneQuixote.
github.com/Blu3Eye/detection…

Felipe Duarte retweeted
Following the first part of the #APT29 #NOBELIUM attack, I am picking up from where we last off in the first part, shedding light on the latter components of the #malware infection chain and going through each in-depth.
Your feedback is appreciated:)
blu3eye.gitbook.io/malware-i…

Felipe Duarte retweeted

Even More Practical Queries for Identifying Malware Infrastructure with @censysio
This time incorporating Regex to catch sneaky certs used by BianLian, #Qakbot, XTreme Rat + More.
embee-research.ghost.io/prac…
#malware #ThreatIntel

Felipe Duarte retweeted
#BianLian Backdoor.
[+] bazaar.abuse.ch/sample/c775e…
/home/jack/Projects/socks/out/208.123.119.123/443-28689/clientService
C2: 208.123.119.123:443
This backdoor is implemented by the operators of BianLian Ransomware and can be an important detection opportunity to avoid the ultimate impact of these adversaries (Ref: redacted.com/blog/bianlian-r…).
You can hunt for active infrastructure through the HTTP response and SSL certificates of C2 servers, which are already published on ThreatFox thanks to the continuous tracking of @drb_ra 🫡
Shodan query: shodan.io/search?query=hash%… (with a few false-positives to consider).


Felipe Duarte retweeted
A quick DFIR tip for the weekend
Now that notepad on Win 11 saves its states and can open tabs. It means history is saved somewhere :)
Well that somewhere is in %localappdata%\Packages\Microsoft.WindowsNotepad_8wekyb3d8bbwe\LocalState\TabState
A new location to monitor and check for unsaved files that might be used temporarily to copy things.
#dfir