

Official NSFOCUS FuYingLab Twitter account. Security information on APT & botnet.
Joined July 2021
- Tweets52
- Following1
- Followers379
- Likes18


We discovered a new botnet family, gorillabot, which launched more than 300,000 attacks in more than 100 countries and regions.nsfocusglobal.com/over-30000…

1
148
#APT #Gamaredon from Ukraine
"Шановний Володимире Олександровичу!"
18b0b361525bf37fc69e8ab86f3316c2
http[:]//salts.faith48.legolaba[.]ru/USER-ПК/perceived.accdw

Our team capture a new APT group as Actor240524 which targeting Azerbaijan and Israel on July 1, 2024 ,we naming the new type of Trojan program used by the group as ABCloader and ABCsync.
nsfocusglobal.com/new-apt-gr…
We released a tactical analysis report about this #APT #DarkPink campaign
nsfocusglobal.com/apt-group-…
blog.nsfocus.net/aptdarkpink…
Thanks @RexorVc0 and @xanda for sharing!


#APT #DarkPink #CVE202338831
zip files:
dd9146bf793ac34de3825bdabcd9f0f3
5504799eb0e7c186afcb07f7f50775b2
c5331b30587dcaf94bfde94040d4fc89
dropper:
6a3948a3602f11e58d8a9300d50984d6
final payload is #TelePowerBot


FuYingLab retweeted

#APT #DarkPink #Saaiwc CVE-2023-38831 #TelePowerBot #KamiKakaBot #threat #malware
📍🏴
💥🇻🇳🇲🇾
⛓️ #Phishing > RAR + #CVE > Dropp dll > Side-Loading > Injection > Persistence + UAC bypass > Telegram API connection
🔗 Nsfocus Report: blog.nsfocus.net/aptdarkpink…


FuYingLab retweeted

In September, @NSFOCUS_Intl global threat hunting system monitored several new #botnet variant families developed based on #Mirai, among which #hailBot, #kiraiBot and #catDDoS are the most active, are accelerating their spread, and are widely deployed. nsfocusglobal.com/mirai-botn…

FuYingLab retweeted
.@NSFOCUS_Intl discovered a previously unknown advanced persistent threat group targeted victims using an American Red Cross blood drive phishing lure and two novel trojan horse malware tools. #cybersecurity #infosec #ITsecurity
bit.ly/3tadS25

#APT #DarkPink #CVE202338831
zip files:
dd9146bf793ac34de3825bdabcd9f0f3
5504799eb0e7c186afcb07f7f50775b2
c5331b30587dcaf94bfde94040d4fc89
dropper:
6a3948a3602f11e58d8a9300d50984d6
final payload is #TelePowerBot
#APT #Gamaredon #maldoc targeting police of Ukraine
file:
358242ac0768977888138a00b9e99b00
remote link:
http[:]//shone.endeavour31.alpansa[.]ru/DESKTOP-3VASB0N/falcon/family.n64


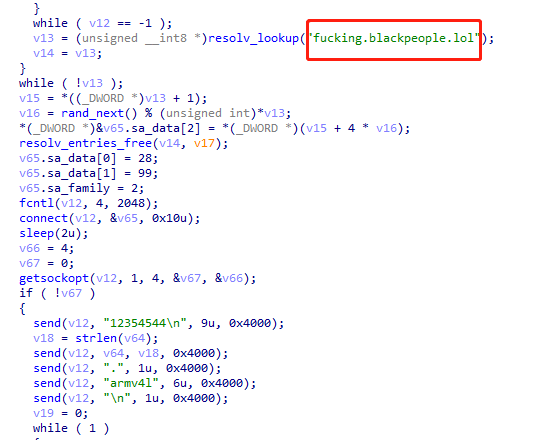

Recently, a new type of Botnet family calling itself #Kirin is spreading widely, which is modified from Gafgyt code but with many new changes.
CC:#37.44.238.182
hash:#43dc824d5c5a0f1dcd5cbbd42c86ce86


"#luoyefeihua", a very large #botnet gang that controls multiple botnet families including #XorDDoS and #Mediocre
blog.nsfocus.net/luoyefeihua…

1
6
599
We recently discovered a new Botnet family written in Golang, which is spread in the name of "#Bins_Bot_hicore" and supports multiple DDoS attack methods. It has gone through multiple version updates. We name this family "hicoreBot".
#GobotV1


You can learn more about #Peacy Botnet through the following article
blog.nsfocus.net/peachy-botn…
Recently, we found that #KekSec gang began to develop #Moobot botnet
string:#watudoinglookingatdis
#w5q6he3dbrsgmclkiu4to18npavj702f
IoC: #15.204.5.85:10275


2
693
We have discovered a new variant of the #Botnet, this family has modified the Mirai online package and is currently very active
Name:#lolmipsel
strings:#pte8cjbdwrmn57g4i6qual20s1k3vfoh

