

Official NSFOCUS FuYingLab Twitter account. Security information on APT & botnet.
Joined July 2021
- Tweets52
- Following1
- Followers379
- Likes18


FuYingLab retweeted

#APT #DarkPink #Saaiwc CVE-2023-38831 #TelePowerBot #KamiKakaBot #threat #malware
📍🏴
💥🇻🇳🇲🇾
⛓️ #Phishing > RAR + #CVE > Dropp dll > Side-Loading > Injection > Persistence + UAC bypass > Telegram API connection
🔗 Nsfocus Report: blog.nsfocus.net/aptdarkpink…


FuYingLab retweeted

In September, @NSFOCUS_Intl global threat hunting system monitored several new #botnet variant families developed based on #Mirai, among which #hailBot, #kiraiBot and #catDDoS are the most active, are accelerating their spread, and are widely deployed. nsfocusglobal.com/mirai-botn…

FuYingLab retweeted
.@NSFOCUS_Intl discovered a previously unknown advanced persistent threat group targeted victims using an American Red Cross blood drive phishing lure and two novel trojan horse malware tools. #cybersecurity #infosec #ITsecurity
bit.ly/3tadS25

FuYingLab retweeted

Türkiye'nin milli projesi denizaltı yönetim sistemi MÜREN'e yönelik siber casusluk operasyonu tespit edilmiş!
Çinli NSFocus'a göre, menşei belirsiz yeni bir APT grubu, 2022 Ağustos ayı başında Deniz Kuvvetleri Komutanlığı (DKK) ve TÜBİTAK'ı hedef almış.
blog.nsfocus.net/murenshark/
FuYingLab retweeted
Lorec53 is a new type of APT group first identified and named by NSFOCUS Security Labs. We sincerely invite you to join in a webinar where our expert will introduce Lorec53's attack methods and types, how we detect and track it and the corresponding security tools and solutions.

FuYingLab retweeted
From the afternoon of February 15, 2022, Ministry of National Defense and Armed Forces of Ukraine, as well as state-owned banks and private banks were reported being attacked by DDoS attacks. NSFOCUS ATH detected relevant attacks, here's our analysis: nsfocusglobal.com/reflective…
FuYingLab retweeted
Recently, NSFOCUS Security Labs captured a large number of phishing files against Ukraine. We confirmed that the series of phishing activities came from the APT group Lorec53. Check our observation and analysis of these attack events: nsfocusglobal.com/apt-lorec5…


FuYingLab retweeted
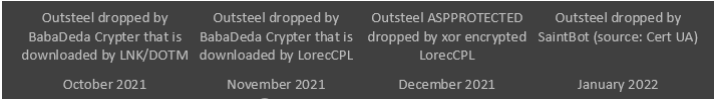
Nice report, we published just some hour after a report similar to ur showing how also babadeda crypter has been employed in those chain telsy.com/babadeda-and-lorec… 😬